Overview
Multi-Factor Authentication (MFA) adds a second layer of security to Acorn logins, requiring users to verify their identity using an authenticator app or SMS in addition to their password.
Enabling MFA for your tenancy
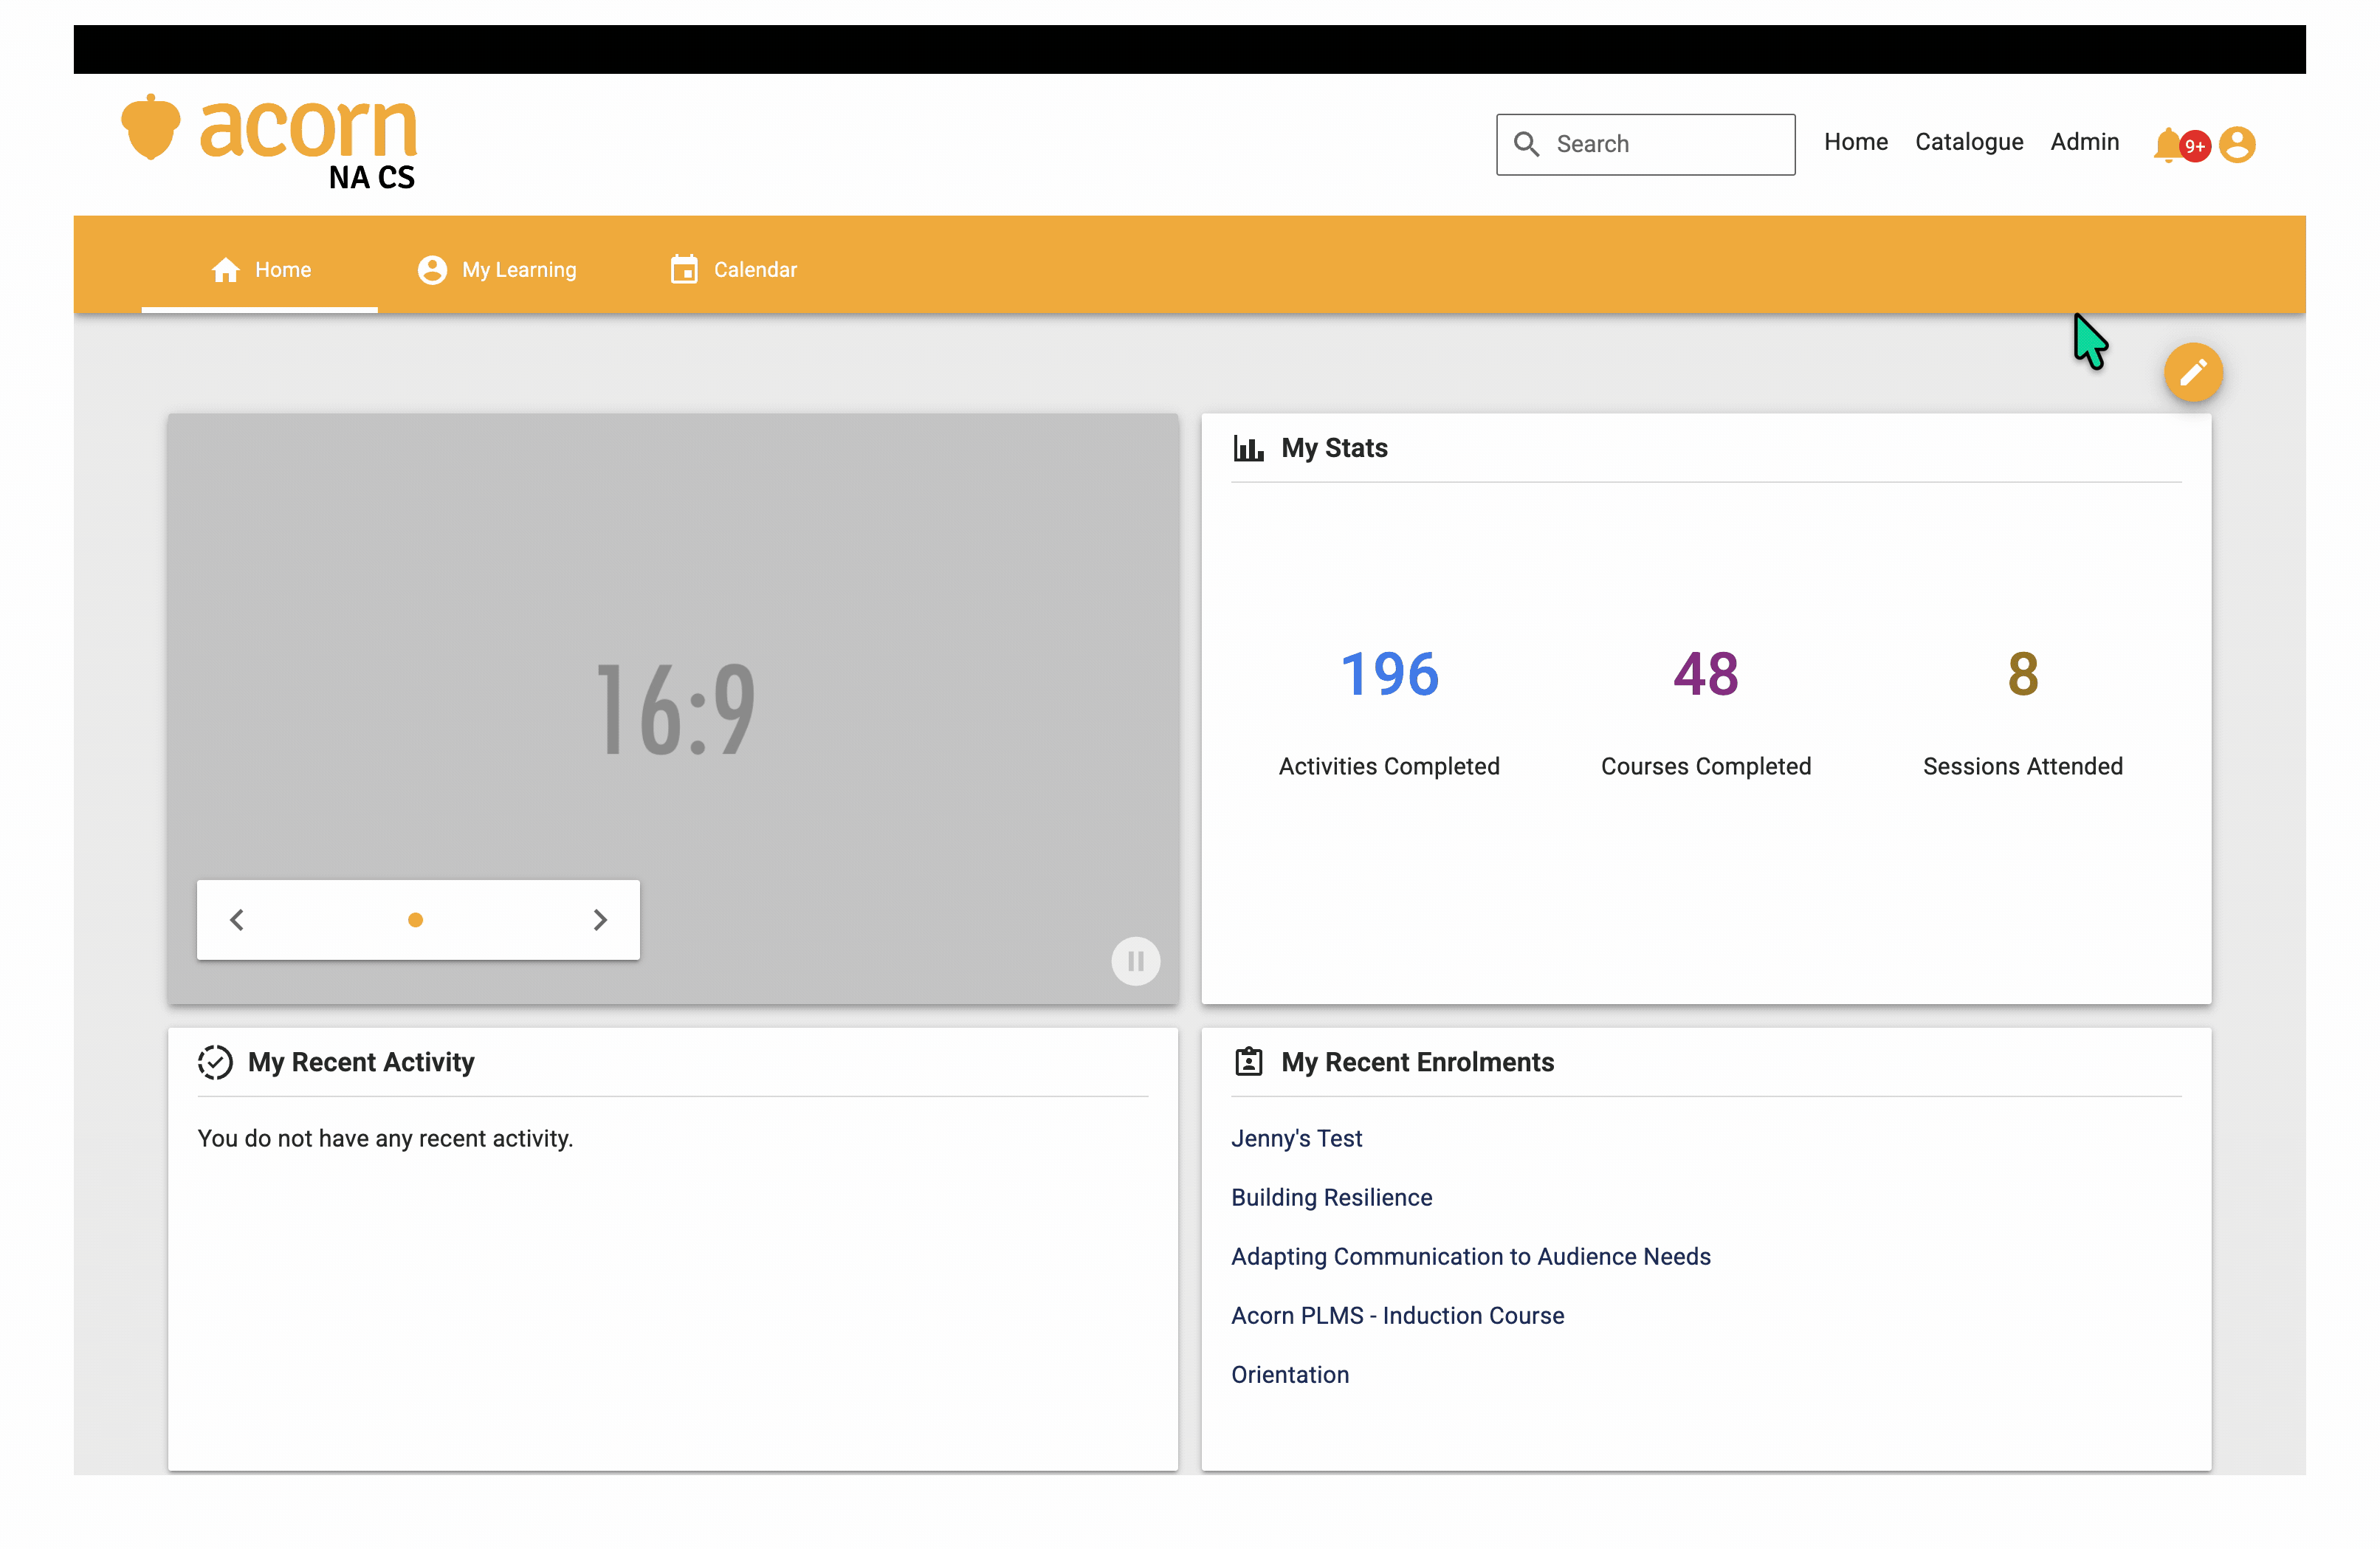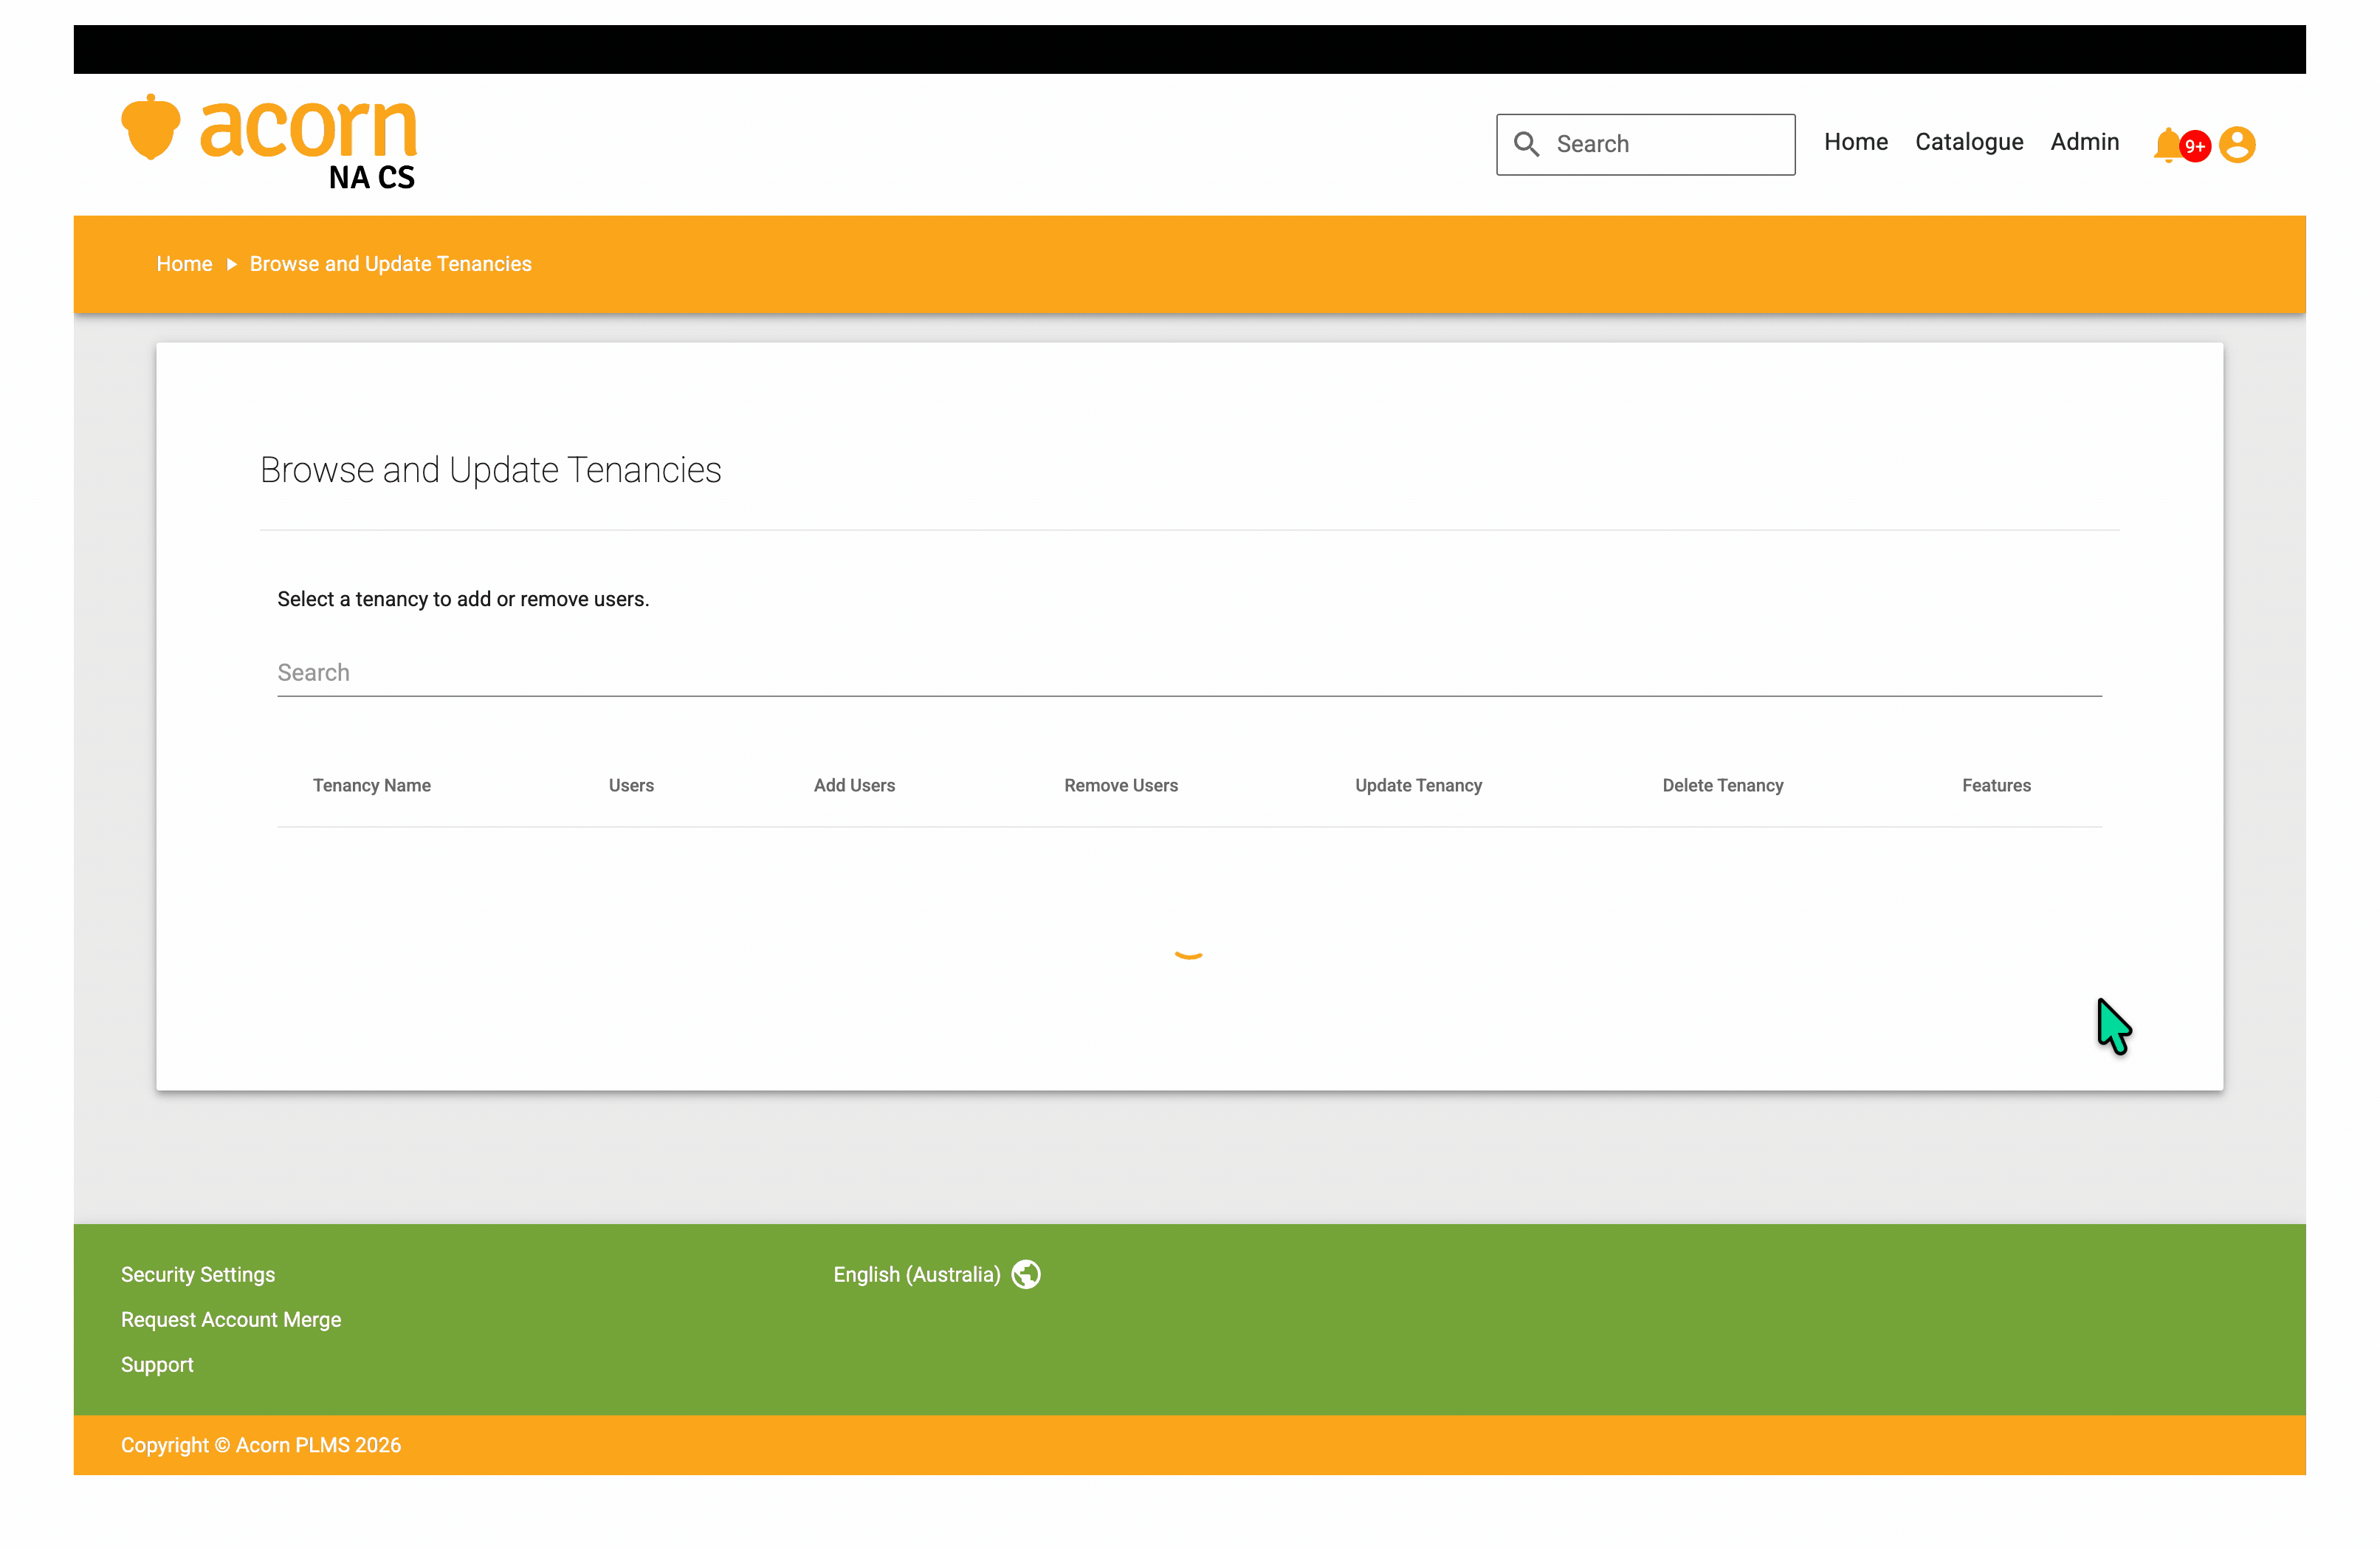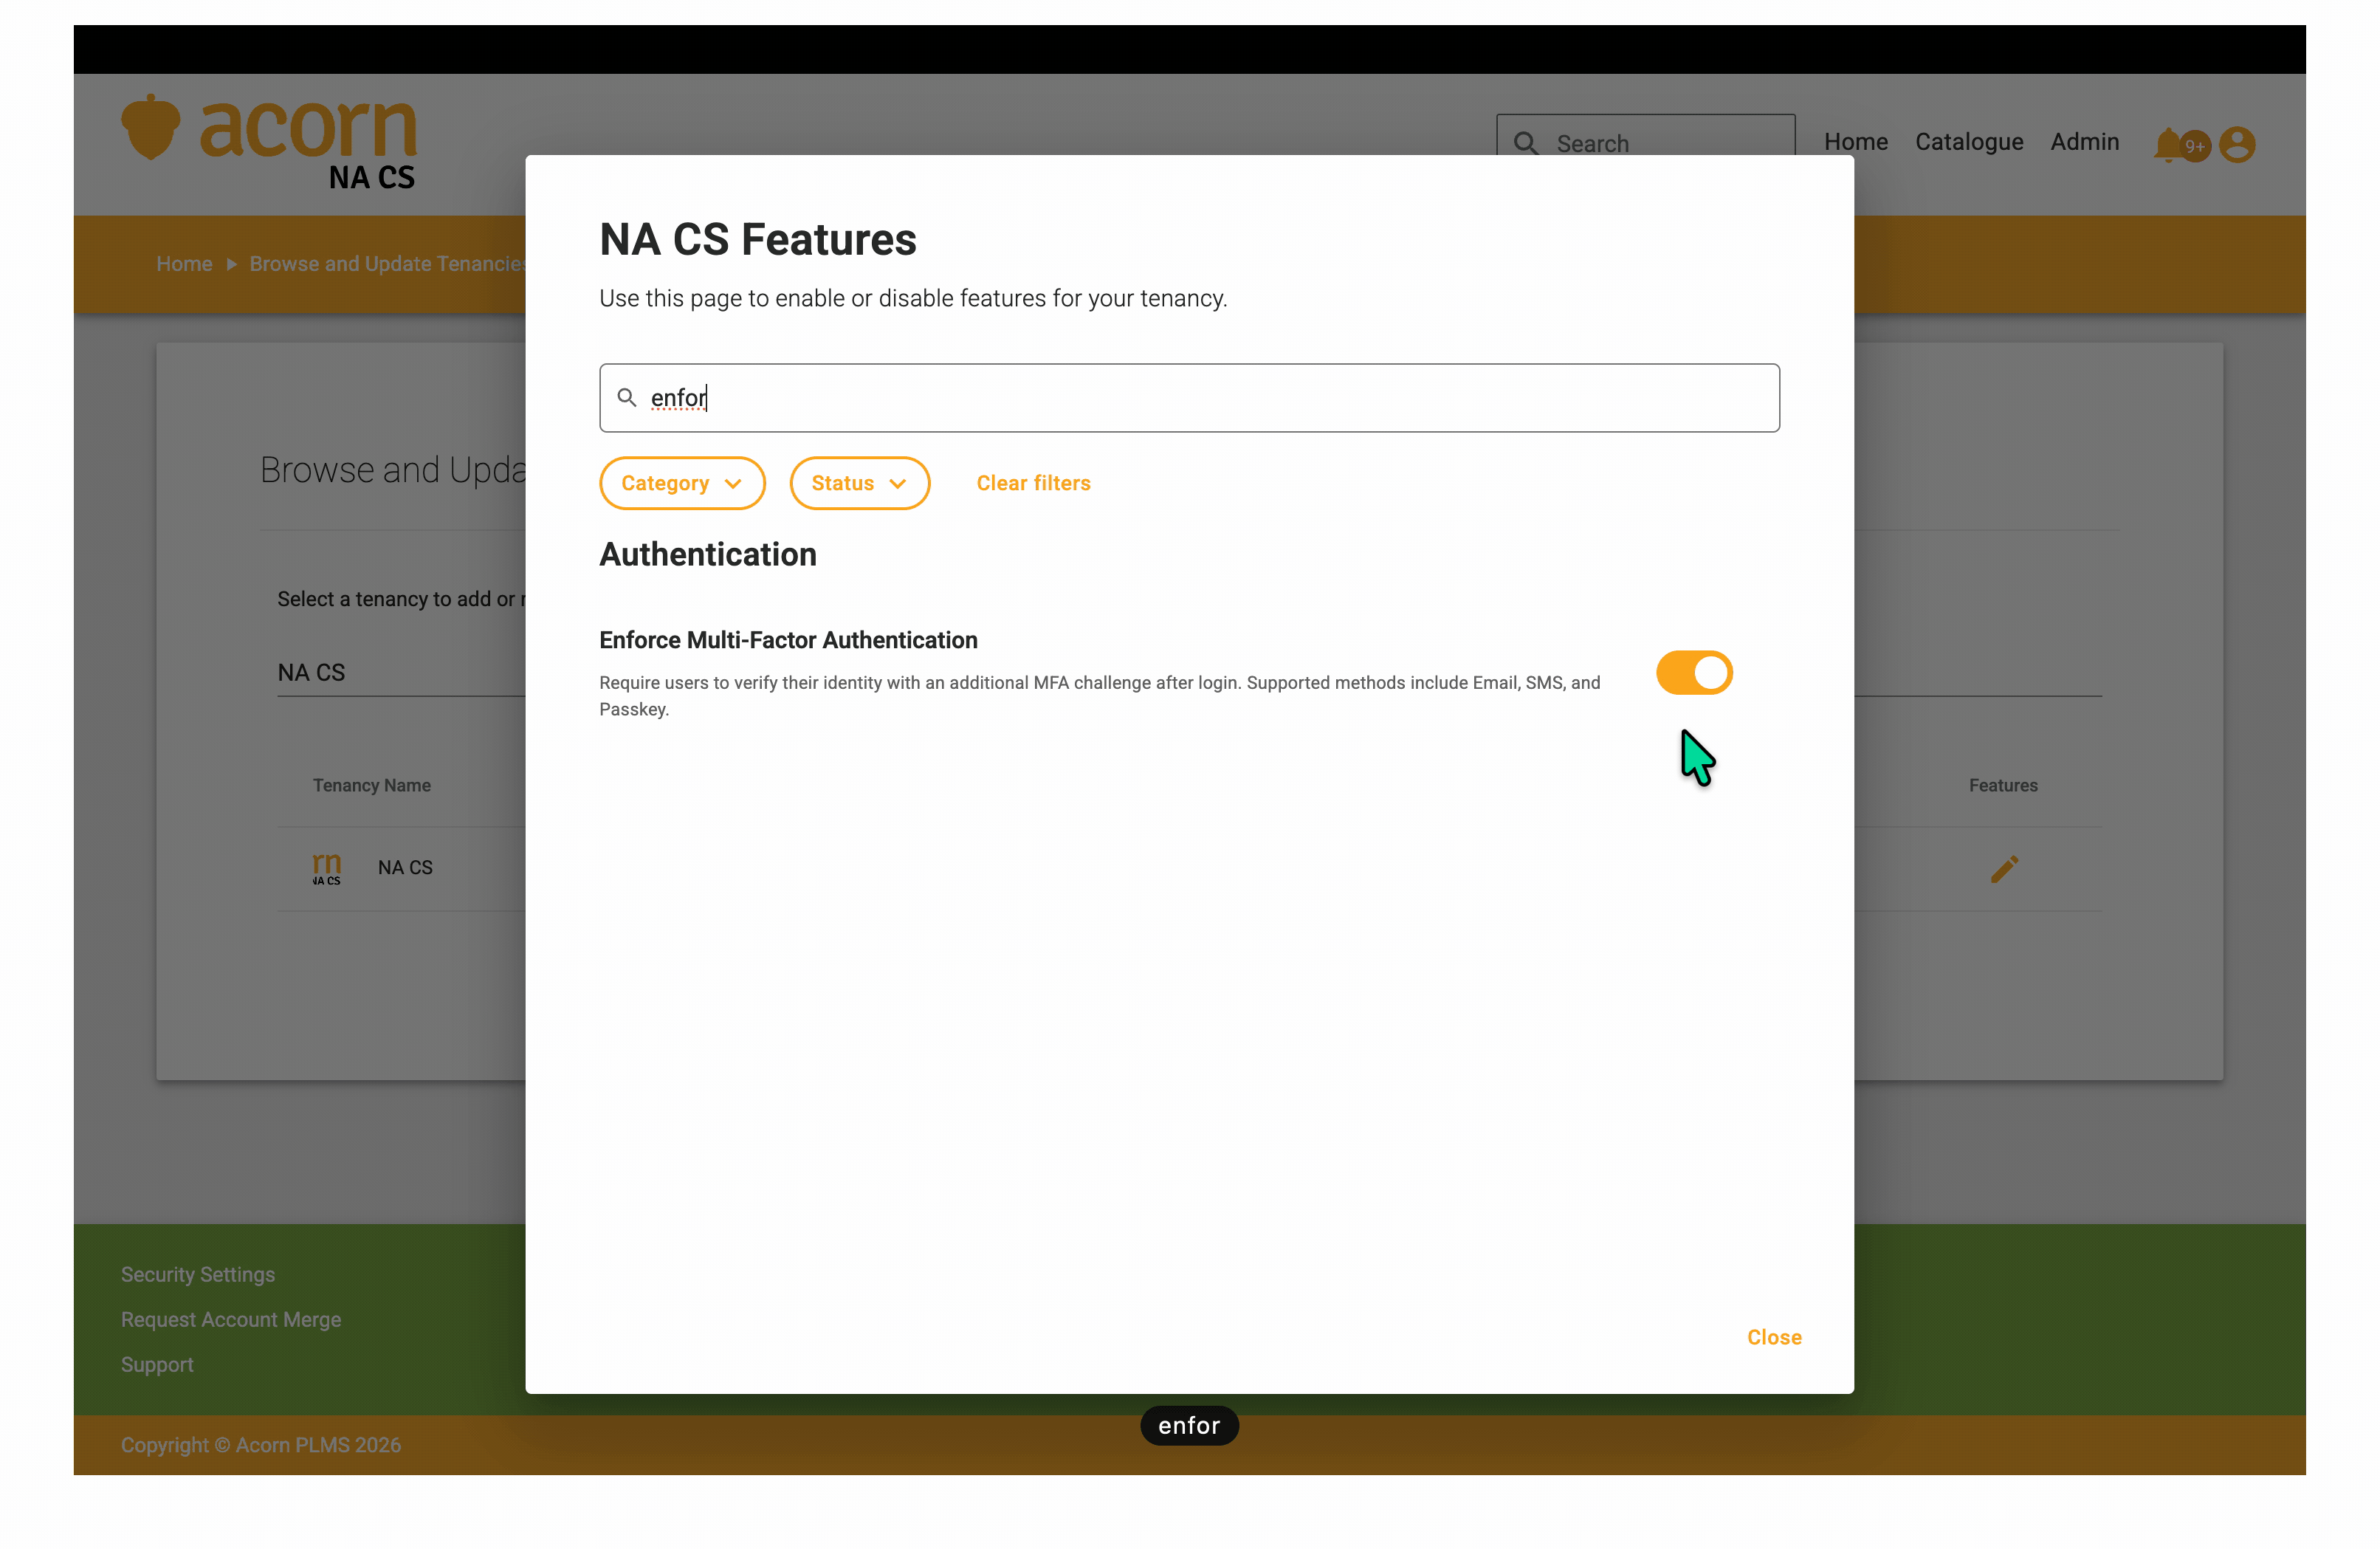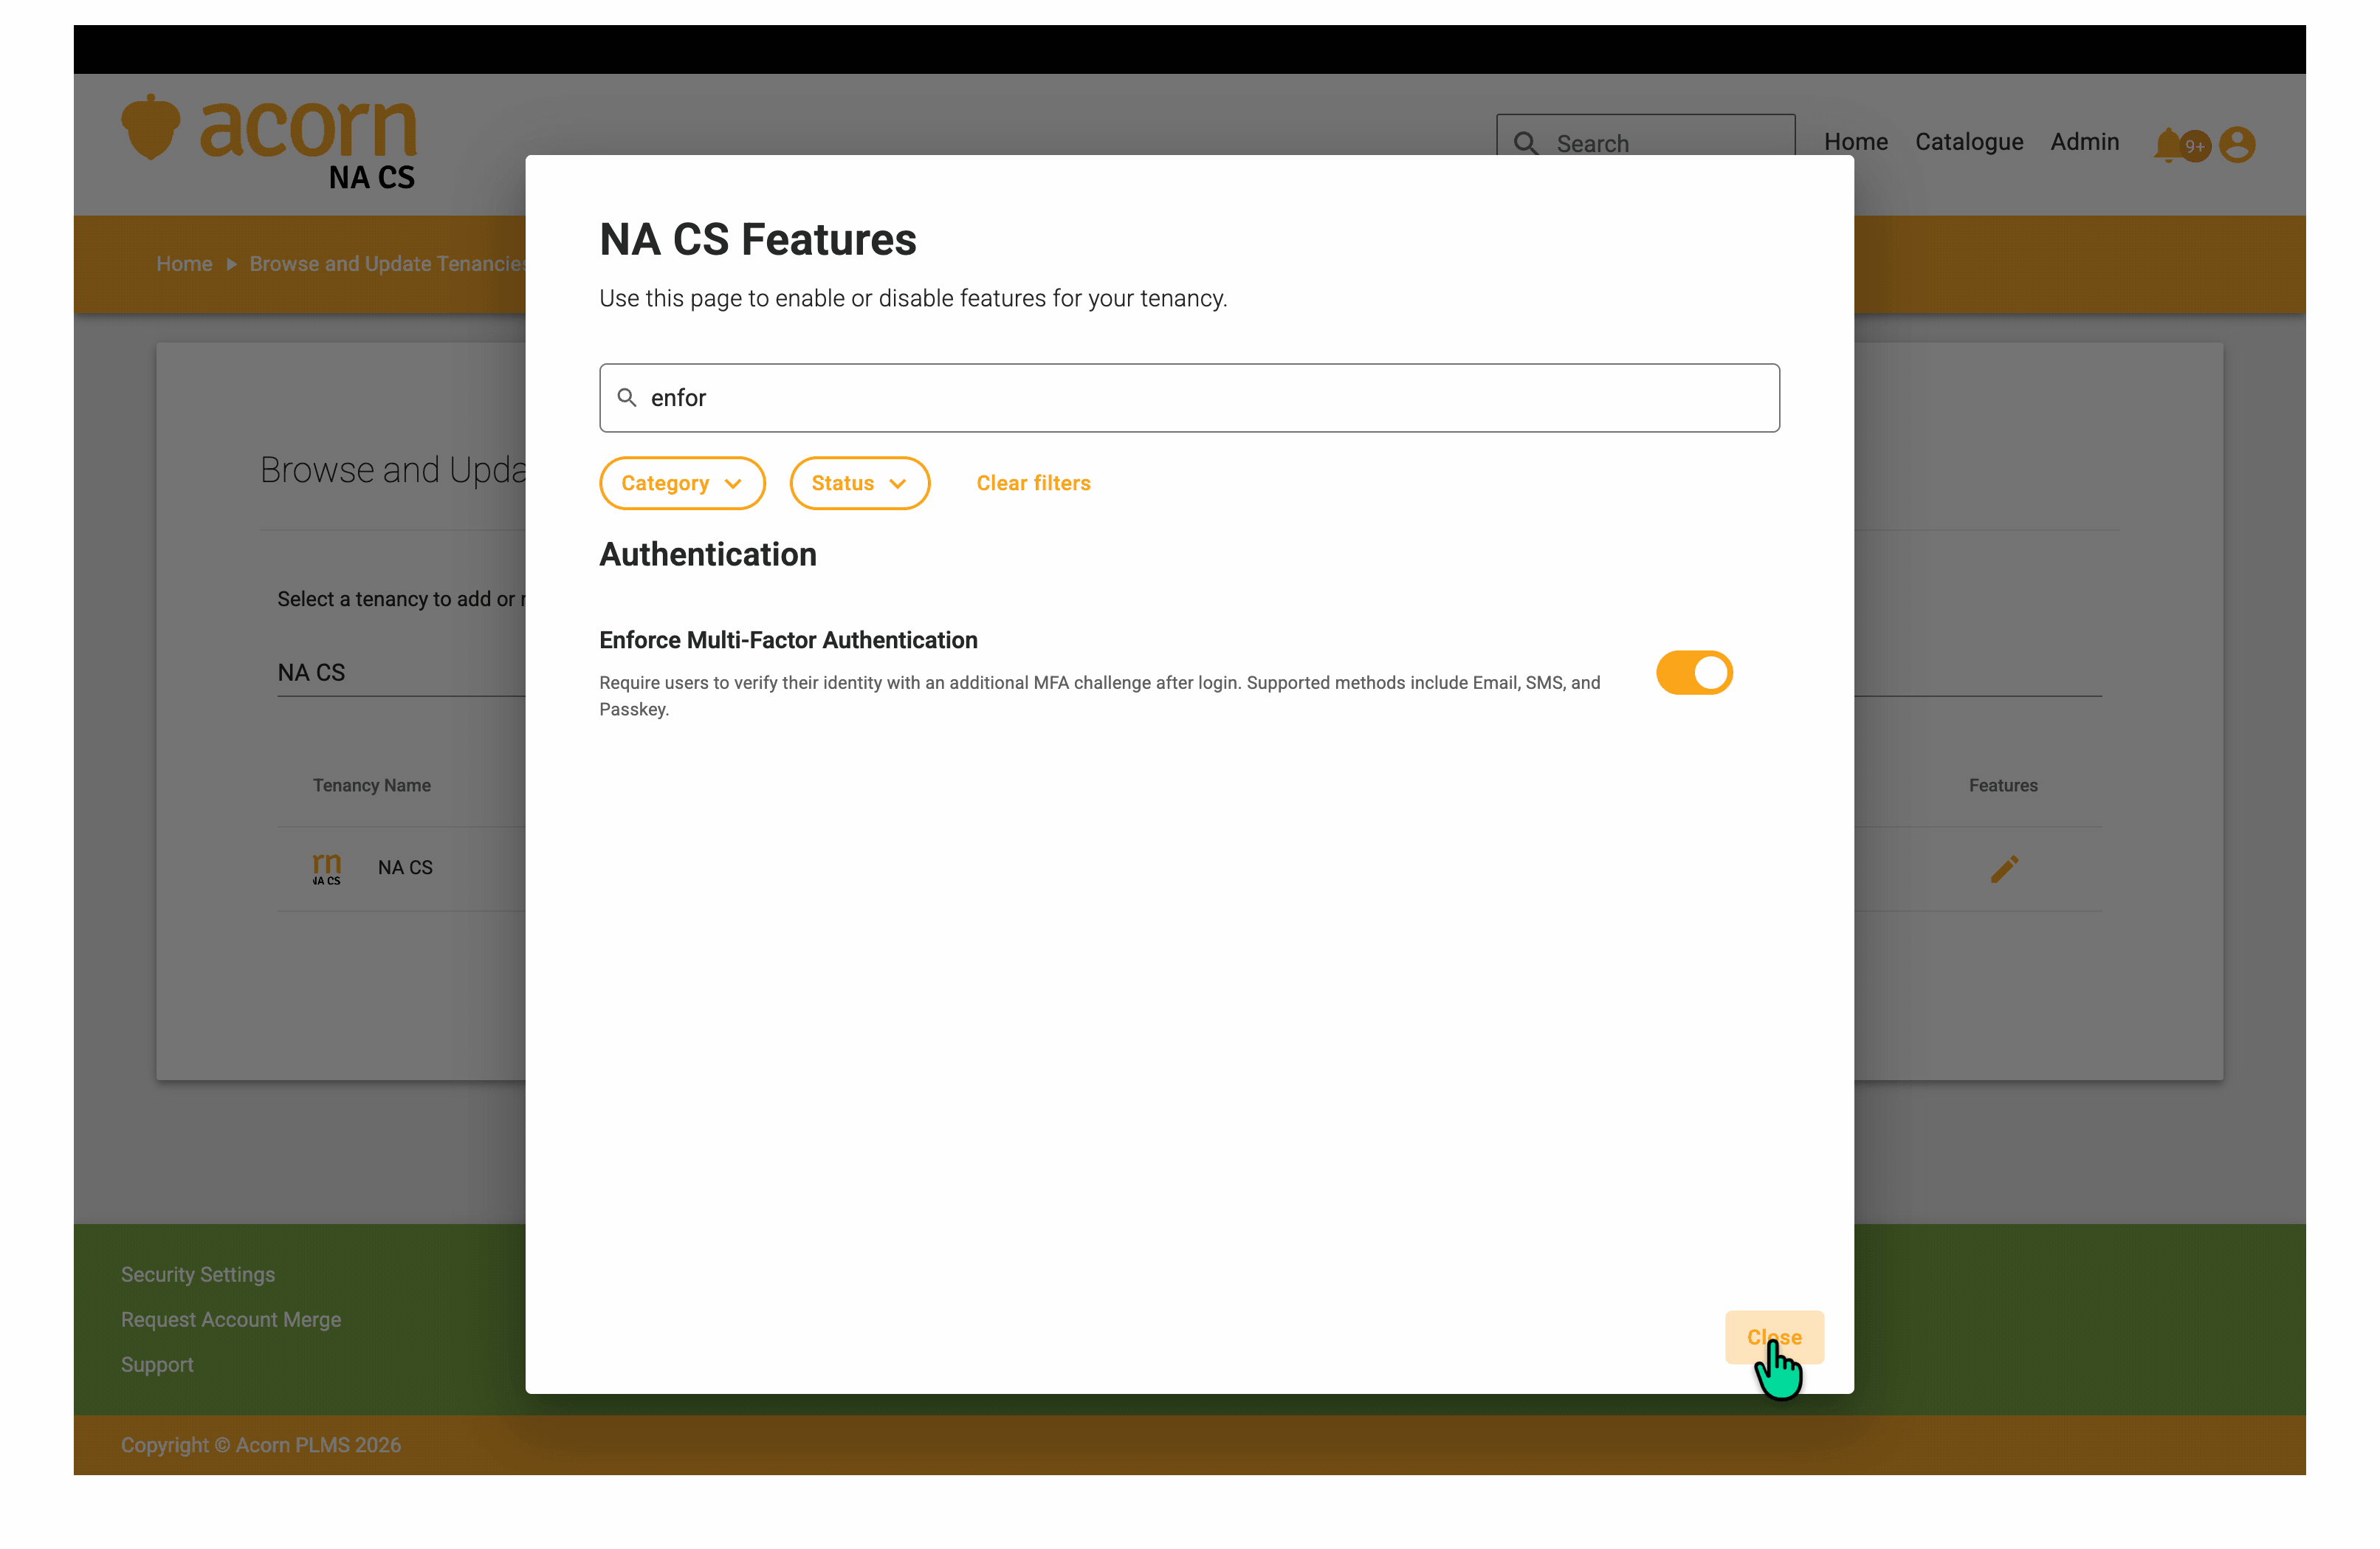
- Go to Admin > Tenancy Management > Browse and Update Tenancies > [Tenancy] > Select pencil
 under Features > Toggle on Enforce Multi-Factor Authentication > Close.
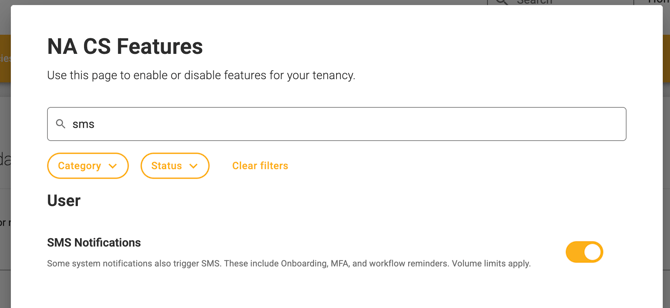
- For SMS as an option, toggle on SMS Notifications.
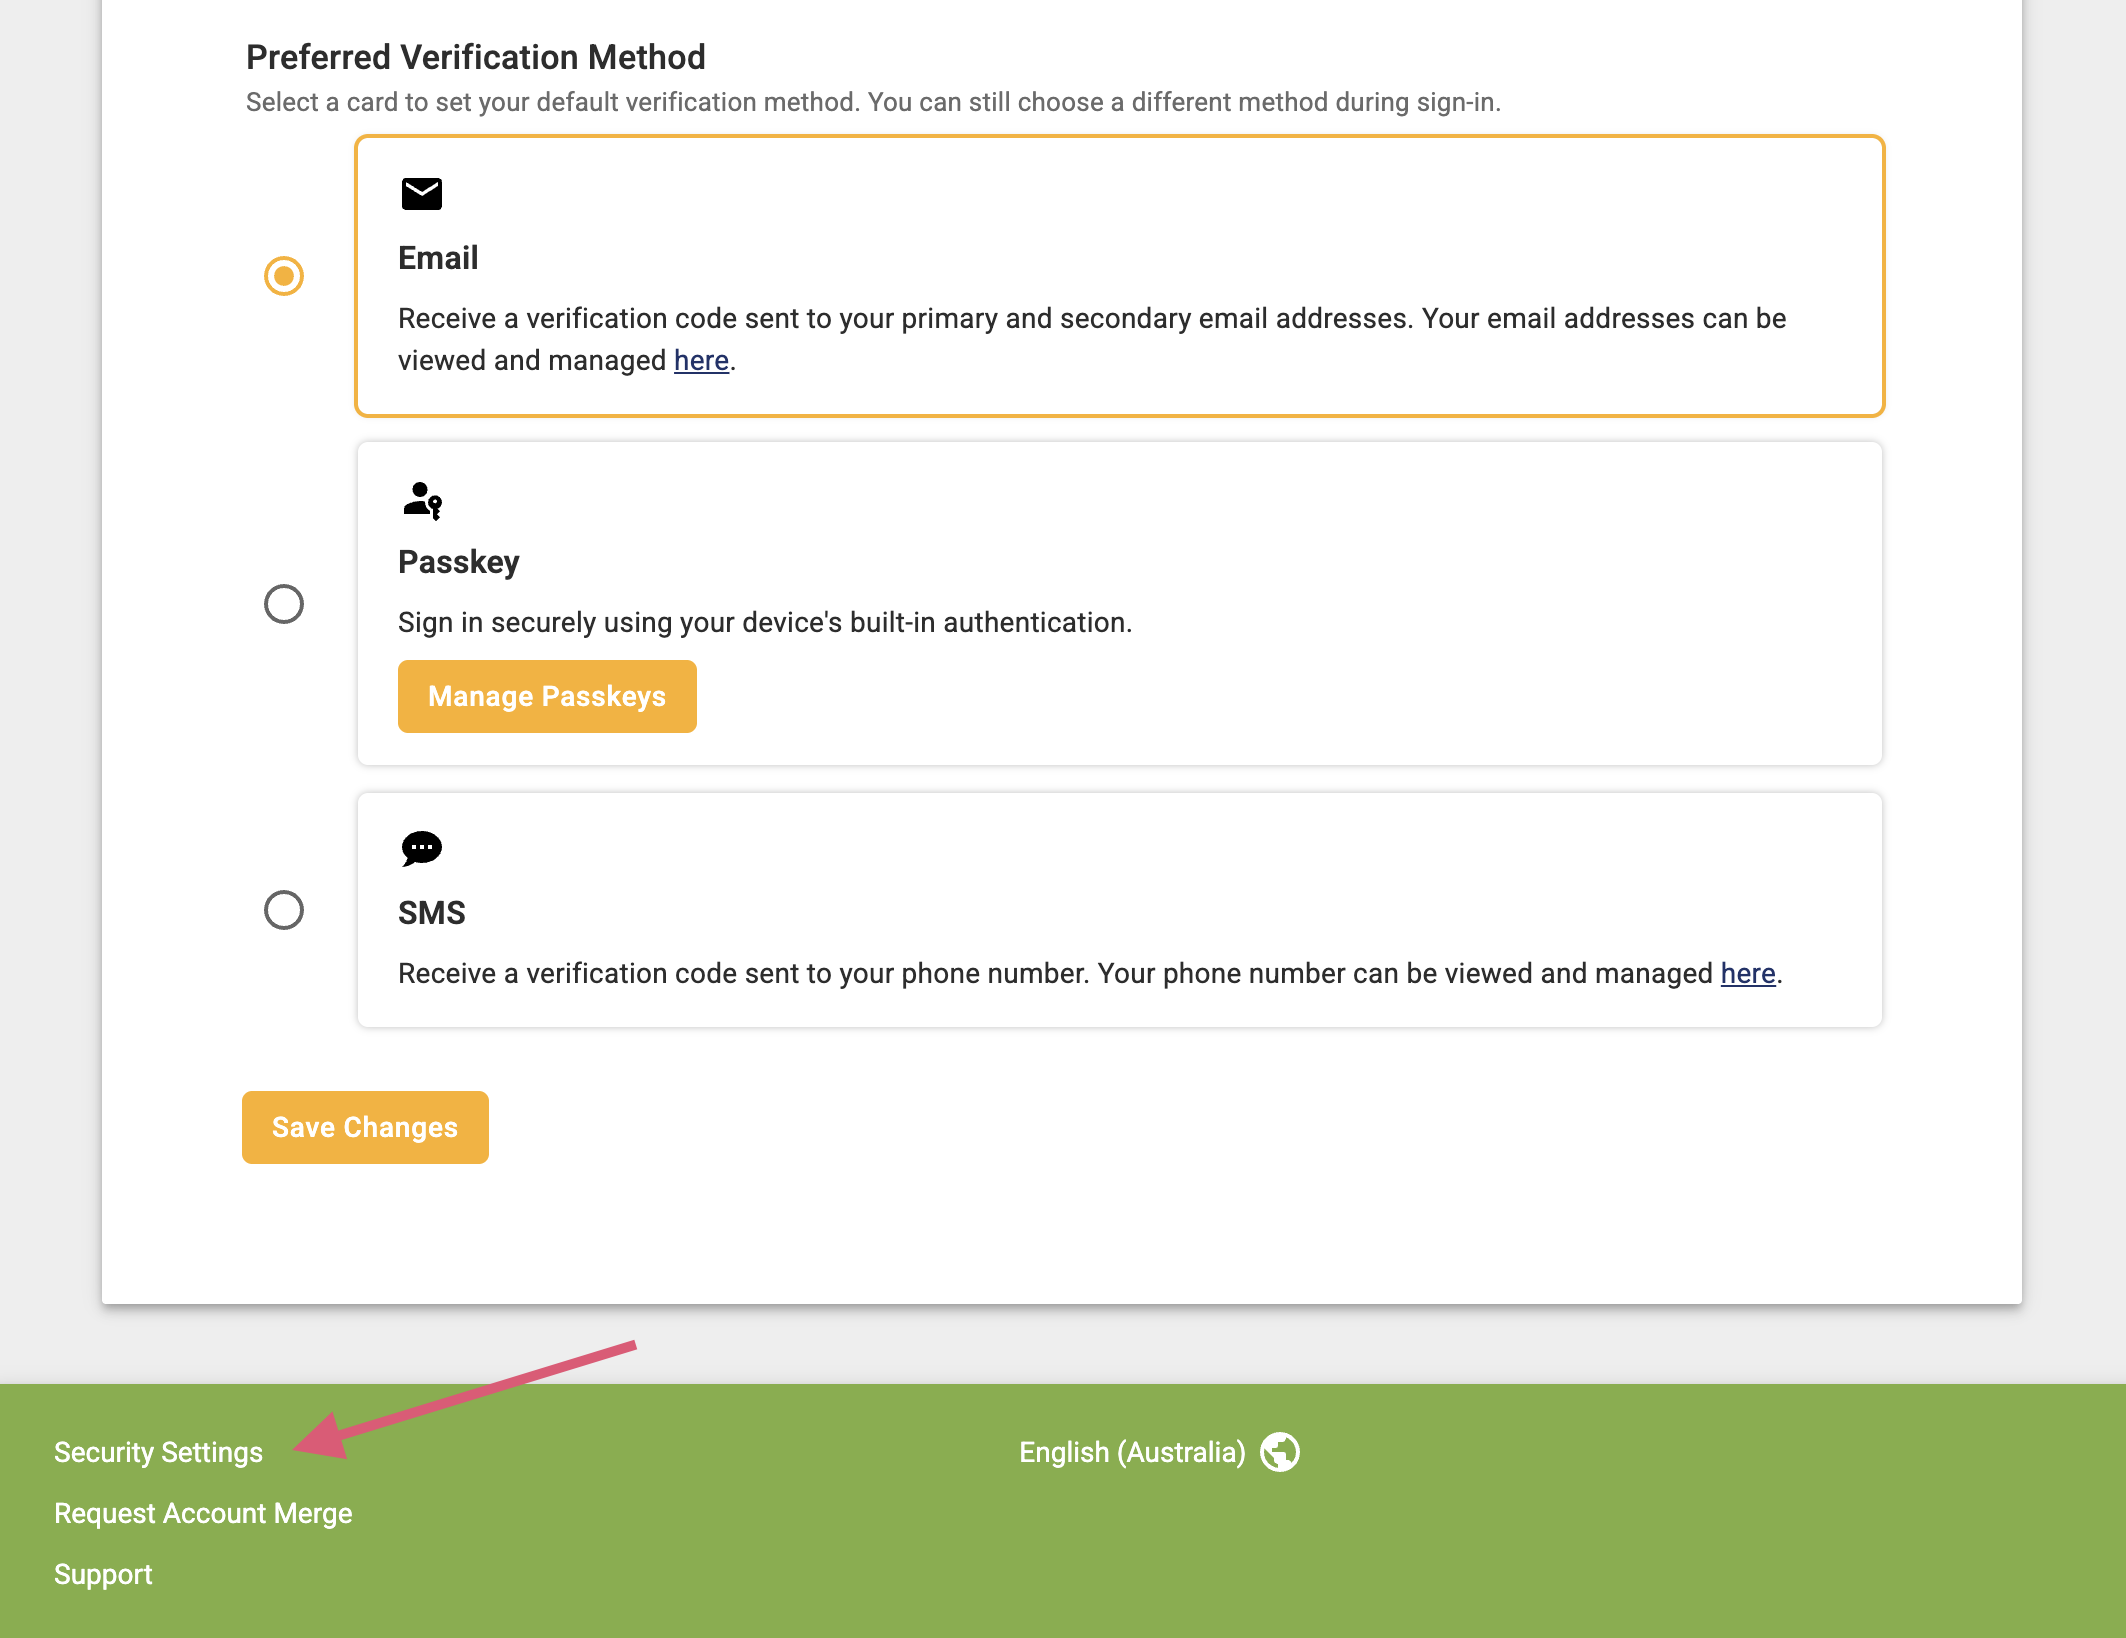
- Users can select their preferred method in Security Settings in the footer of the site. Users can select from Email, Passkey, or SMS.
- For SMS as an option, toggle on SMS Notifications.
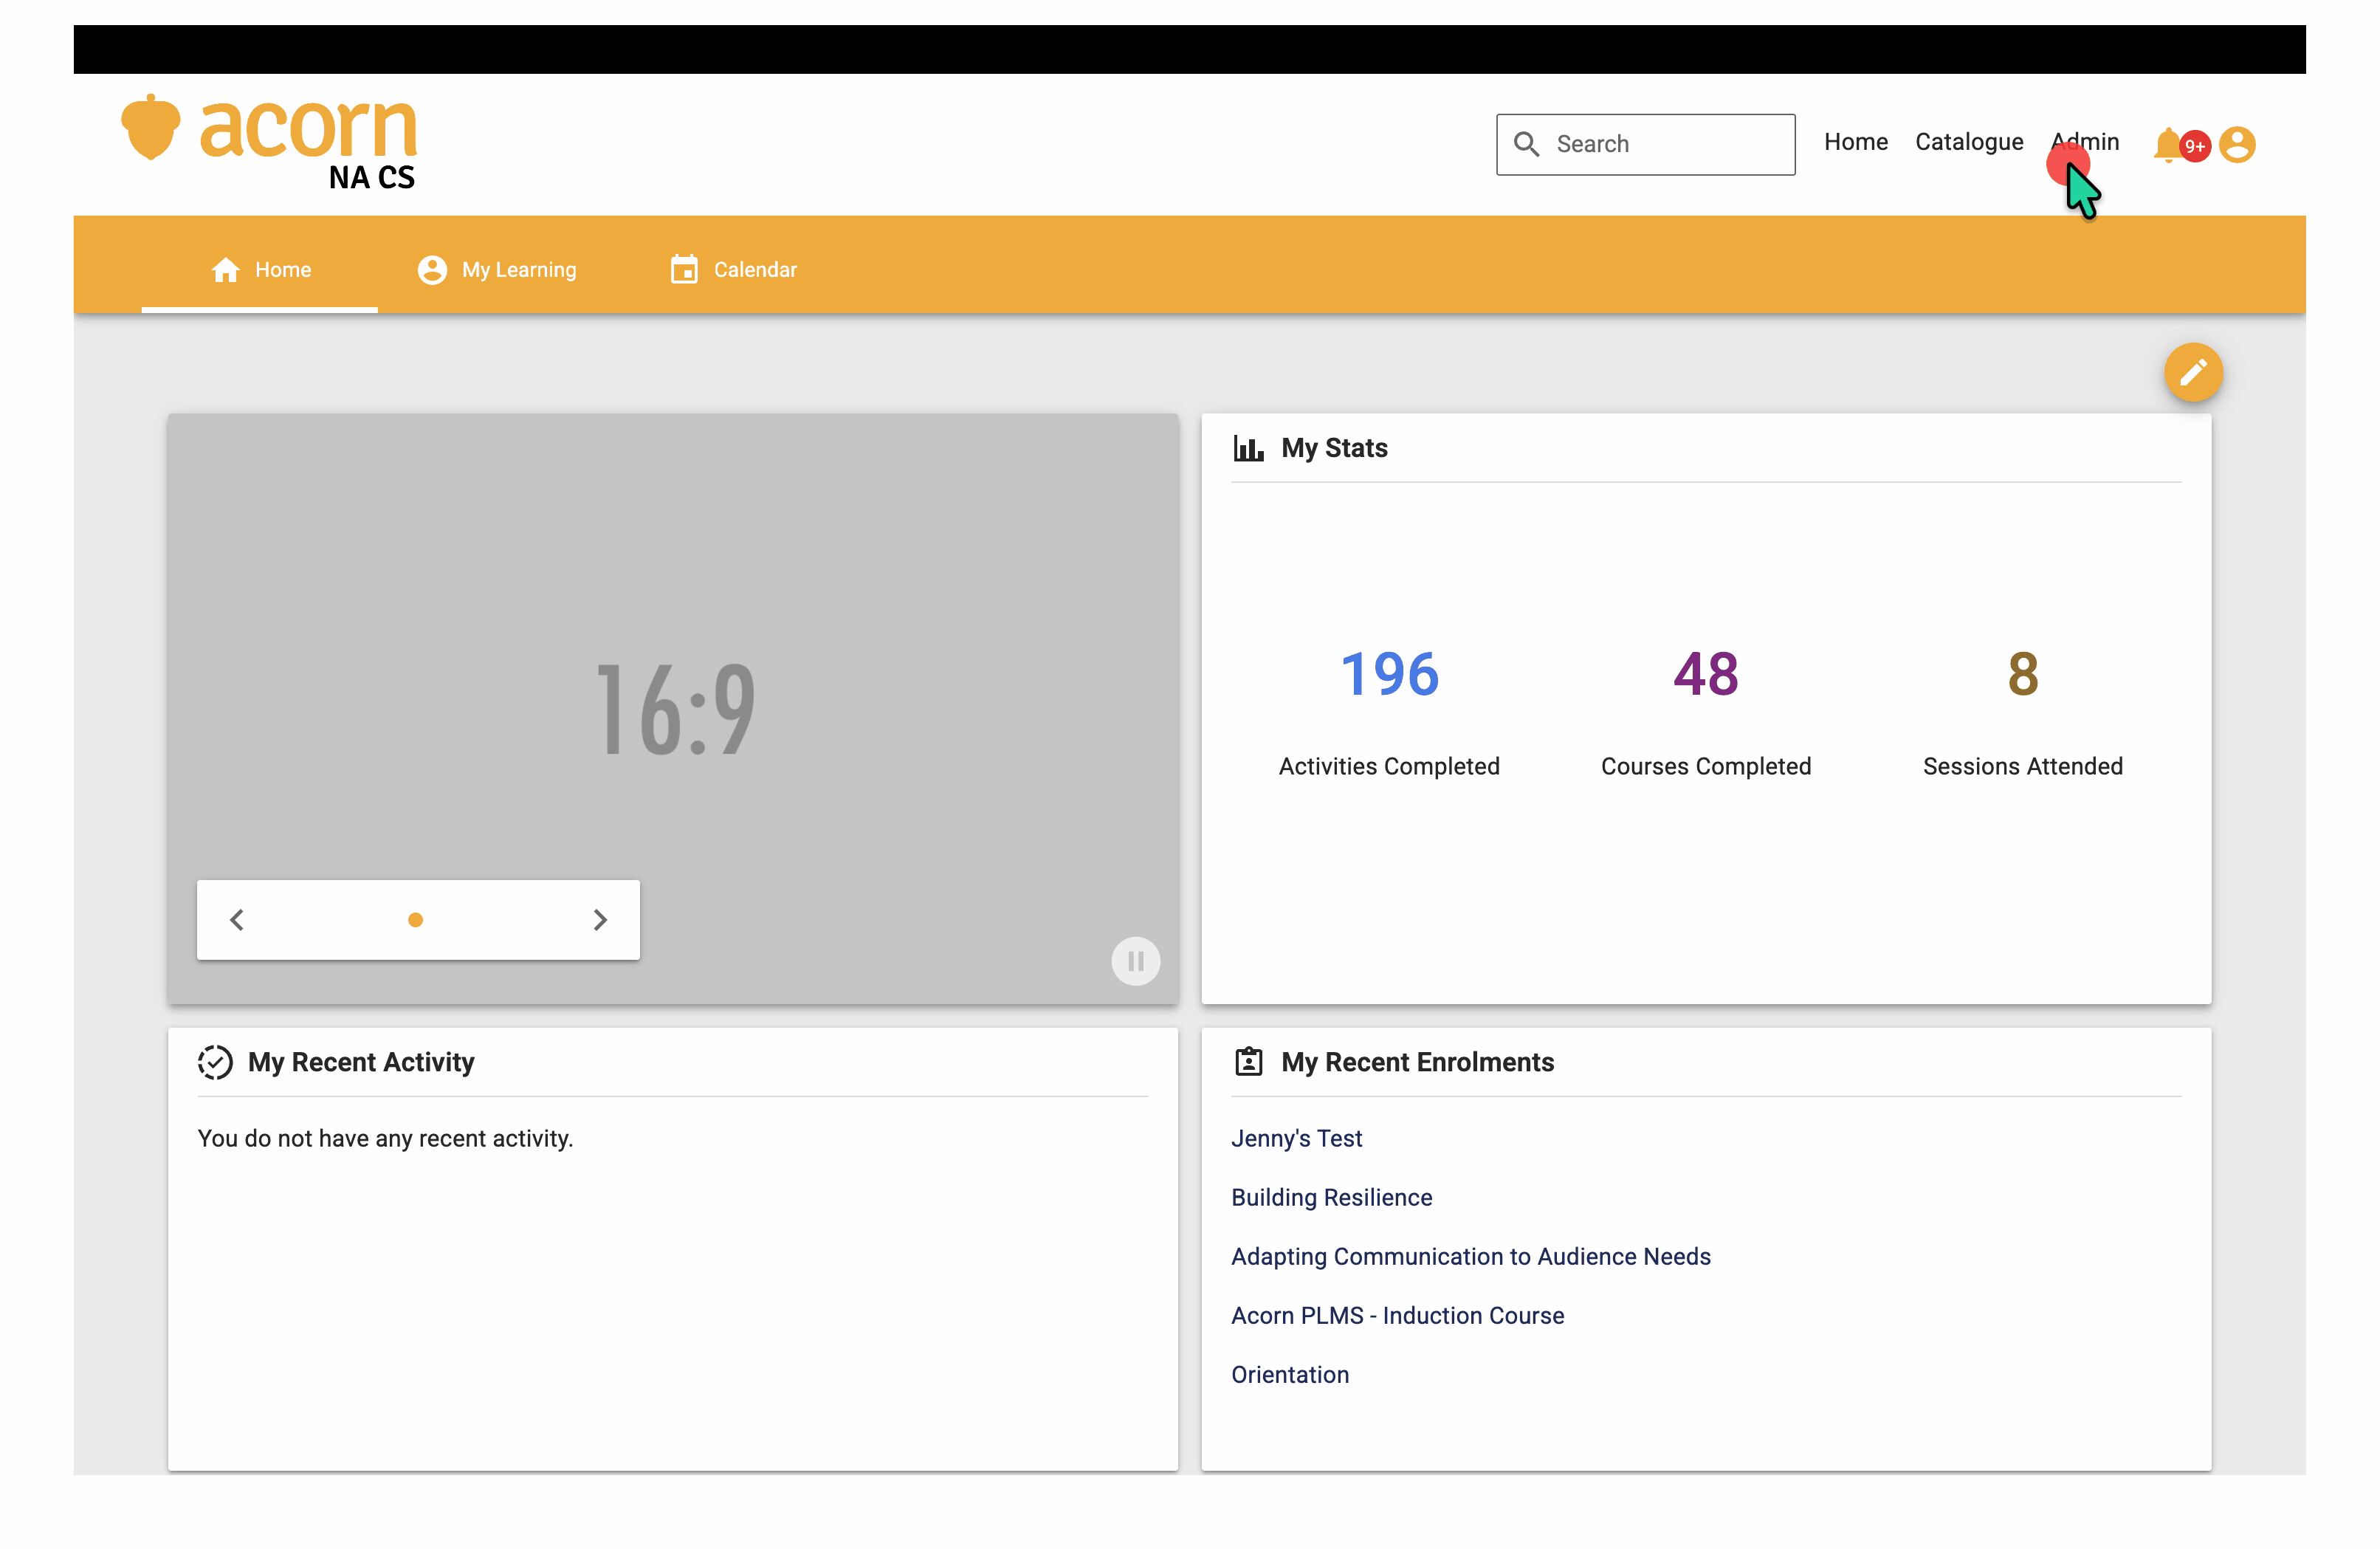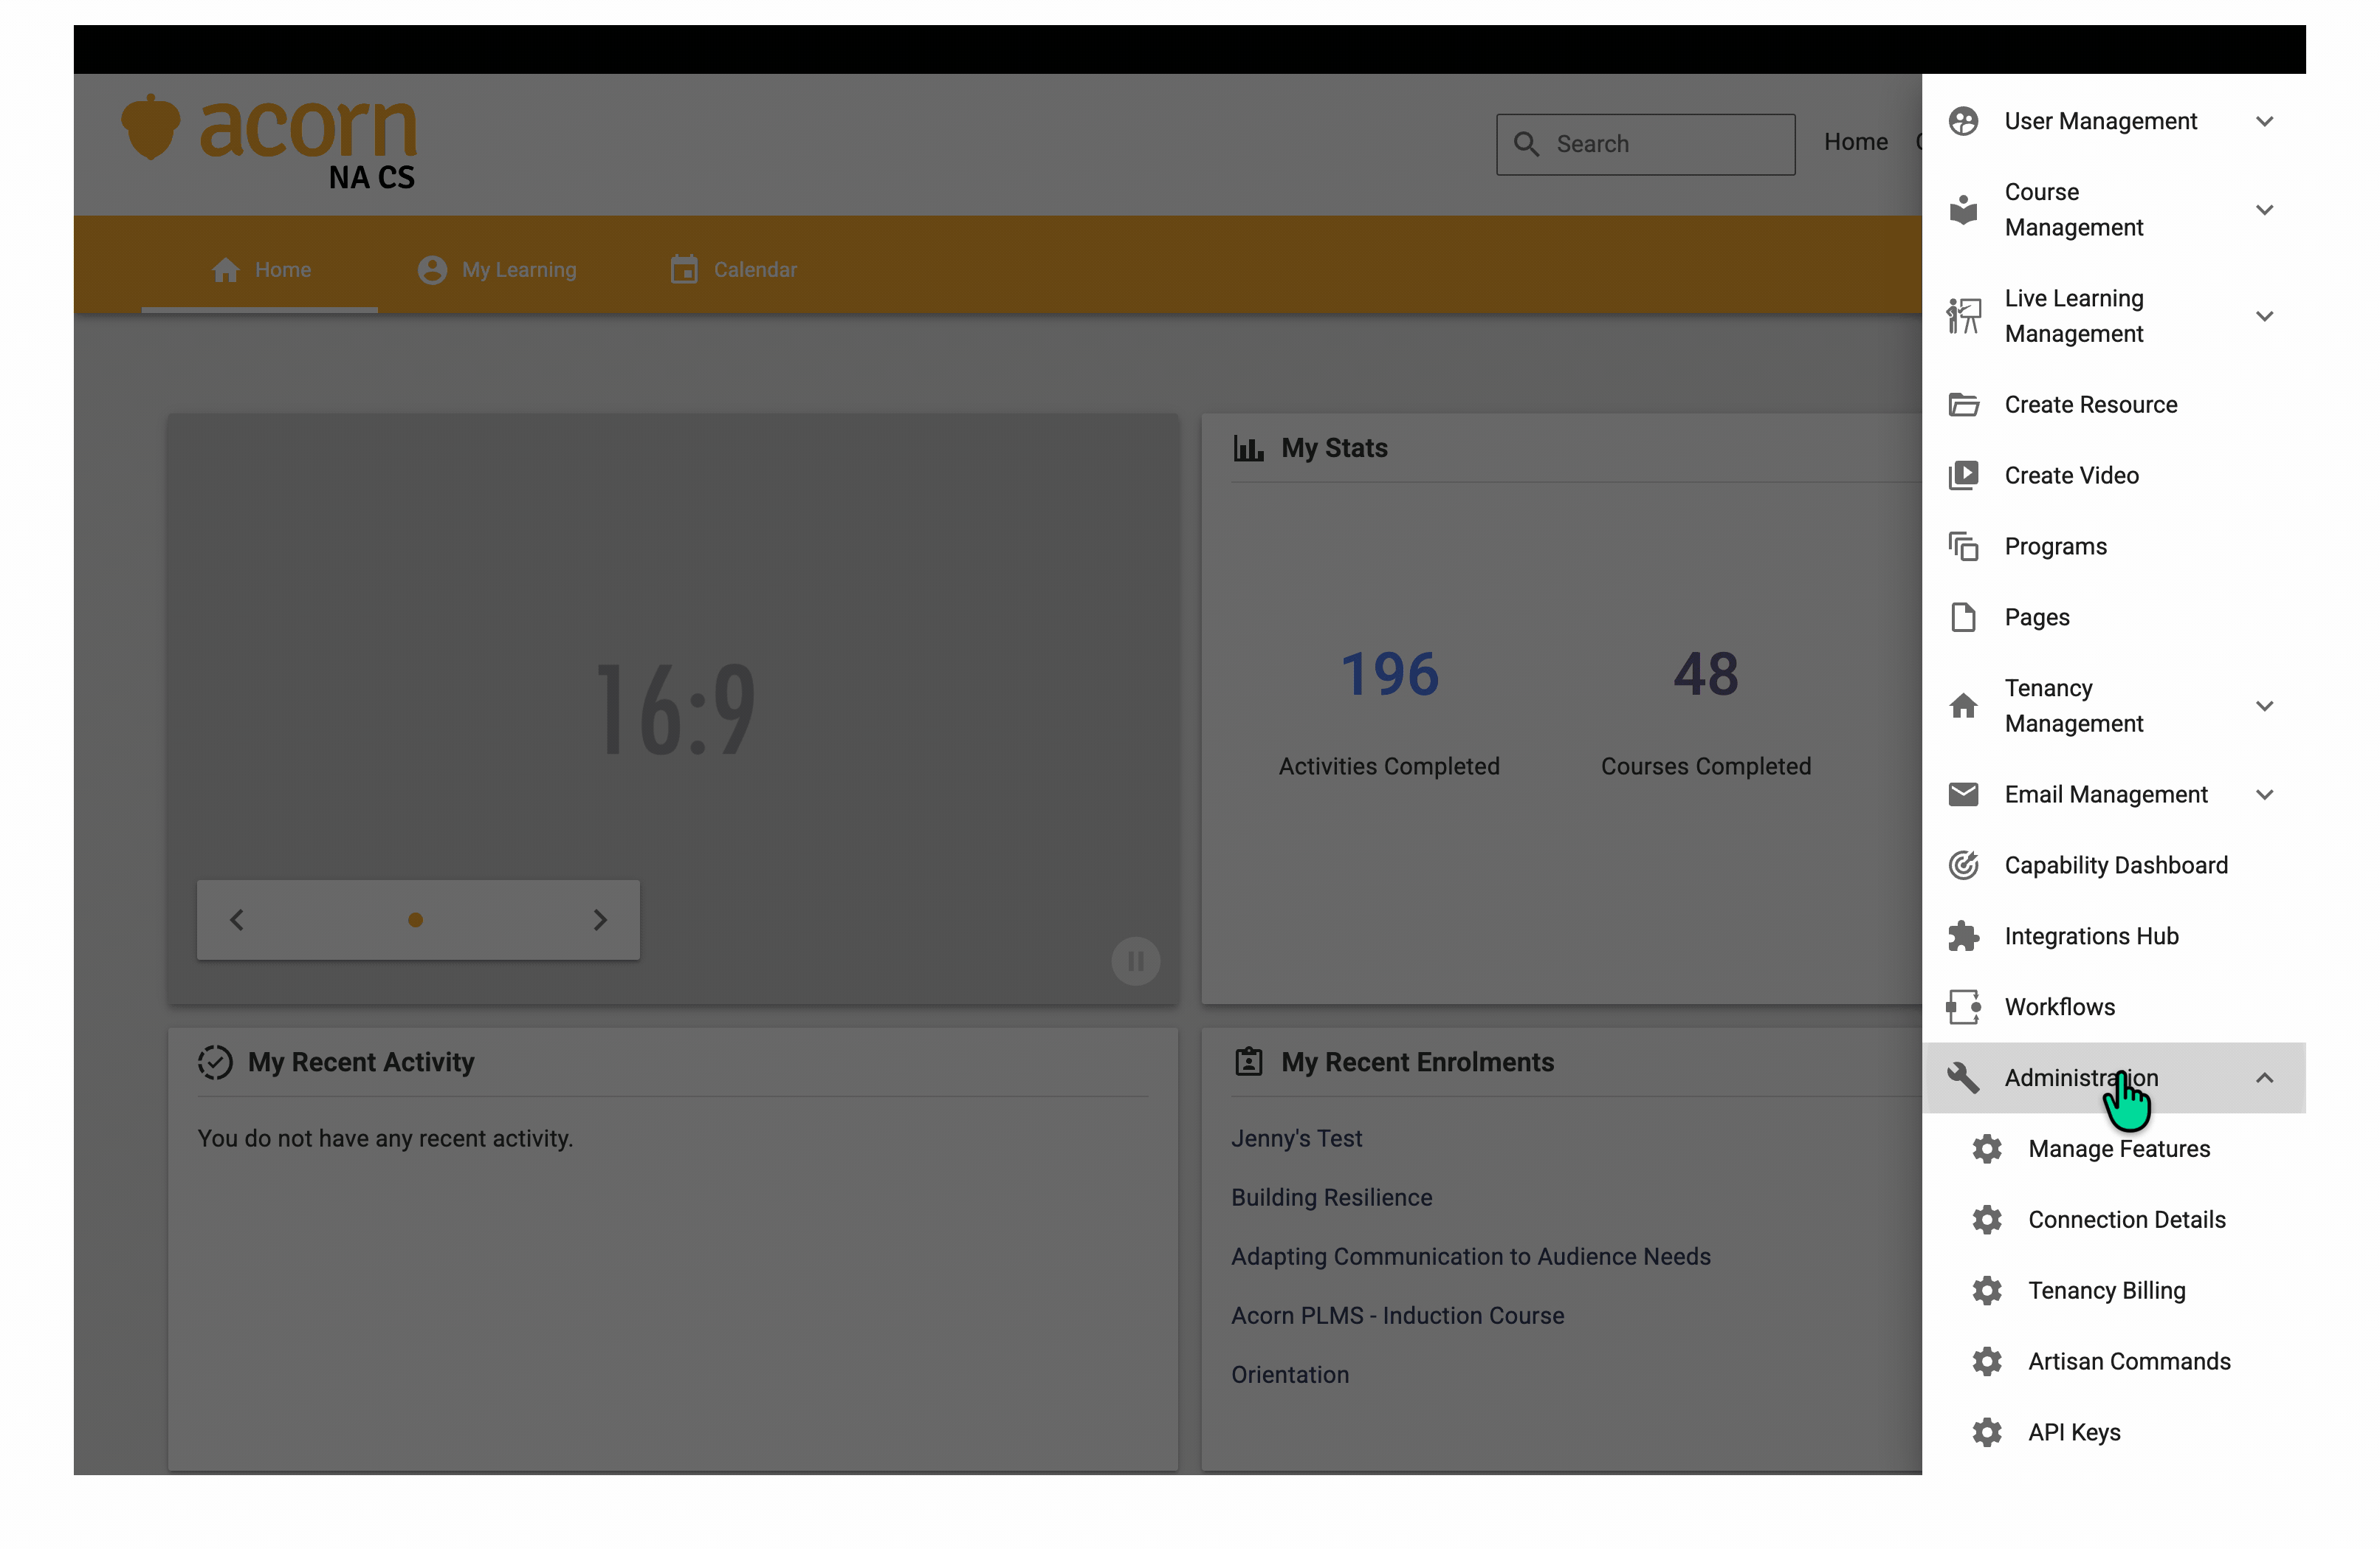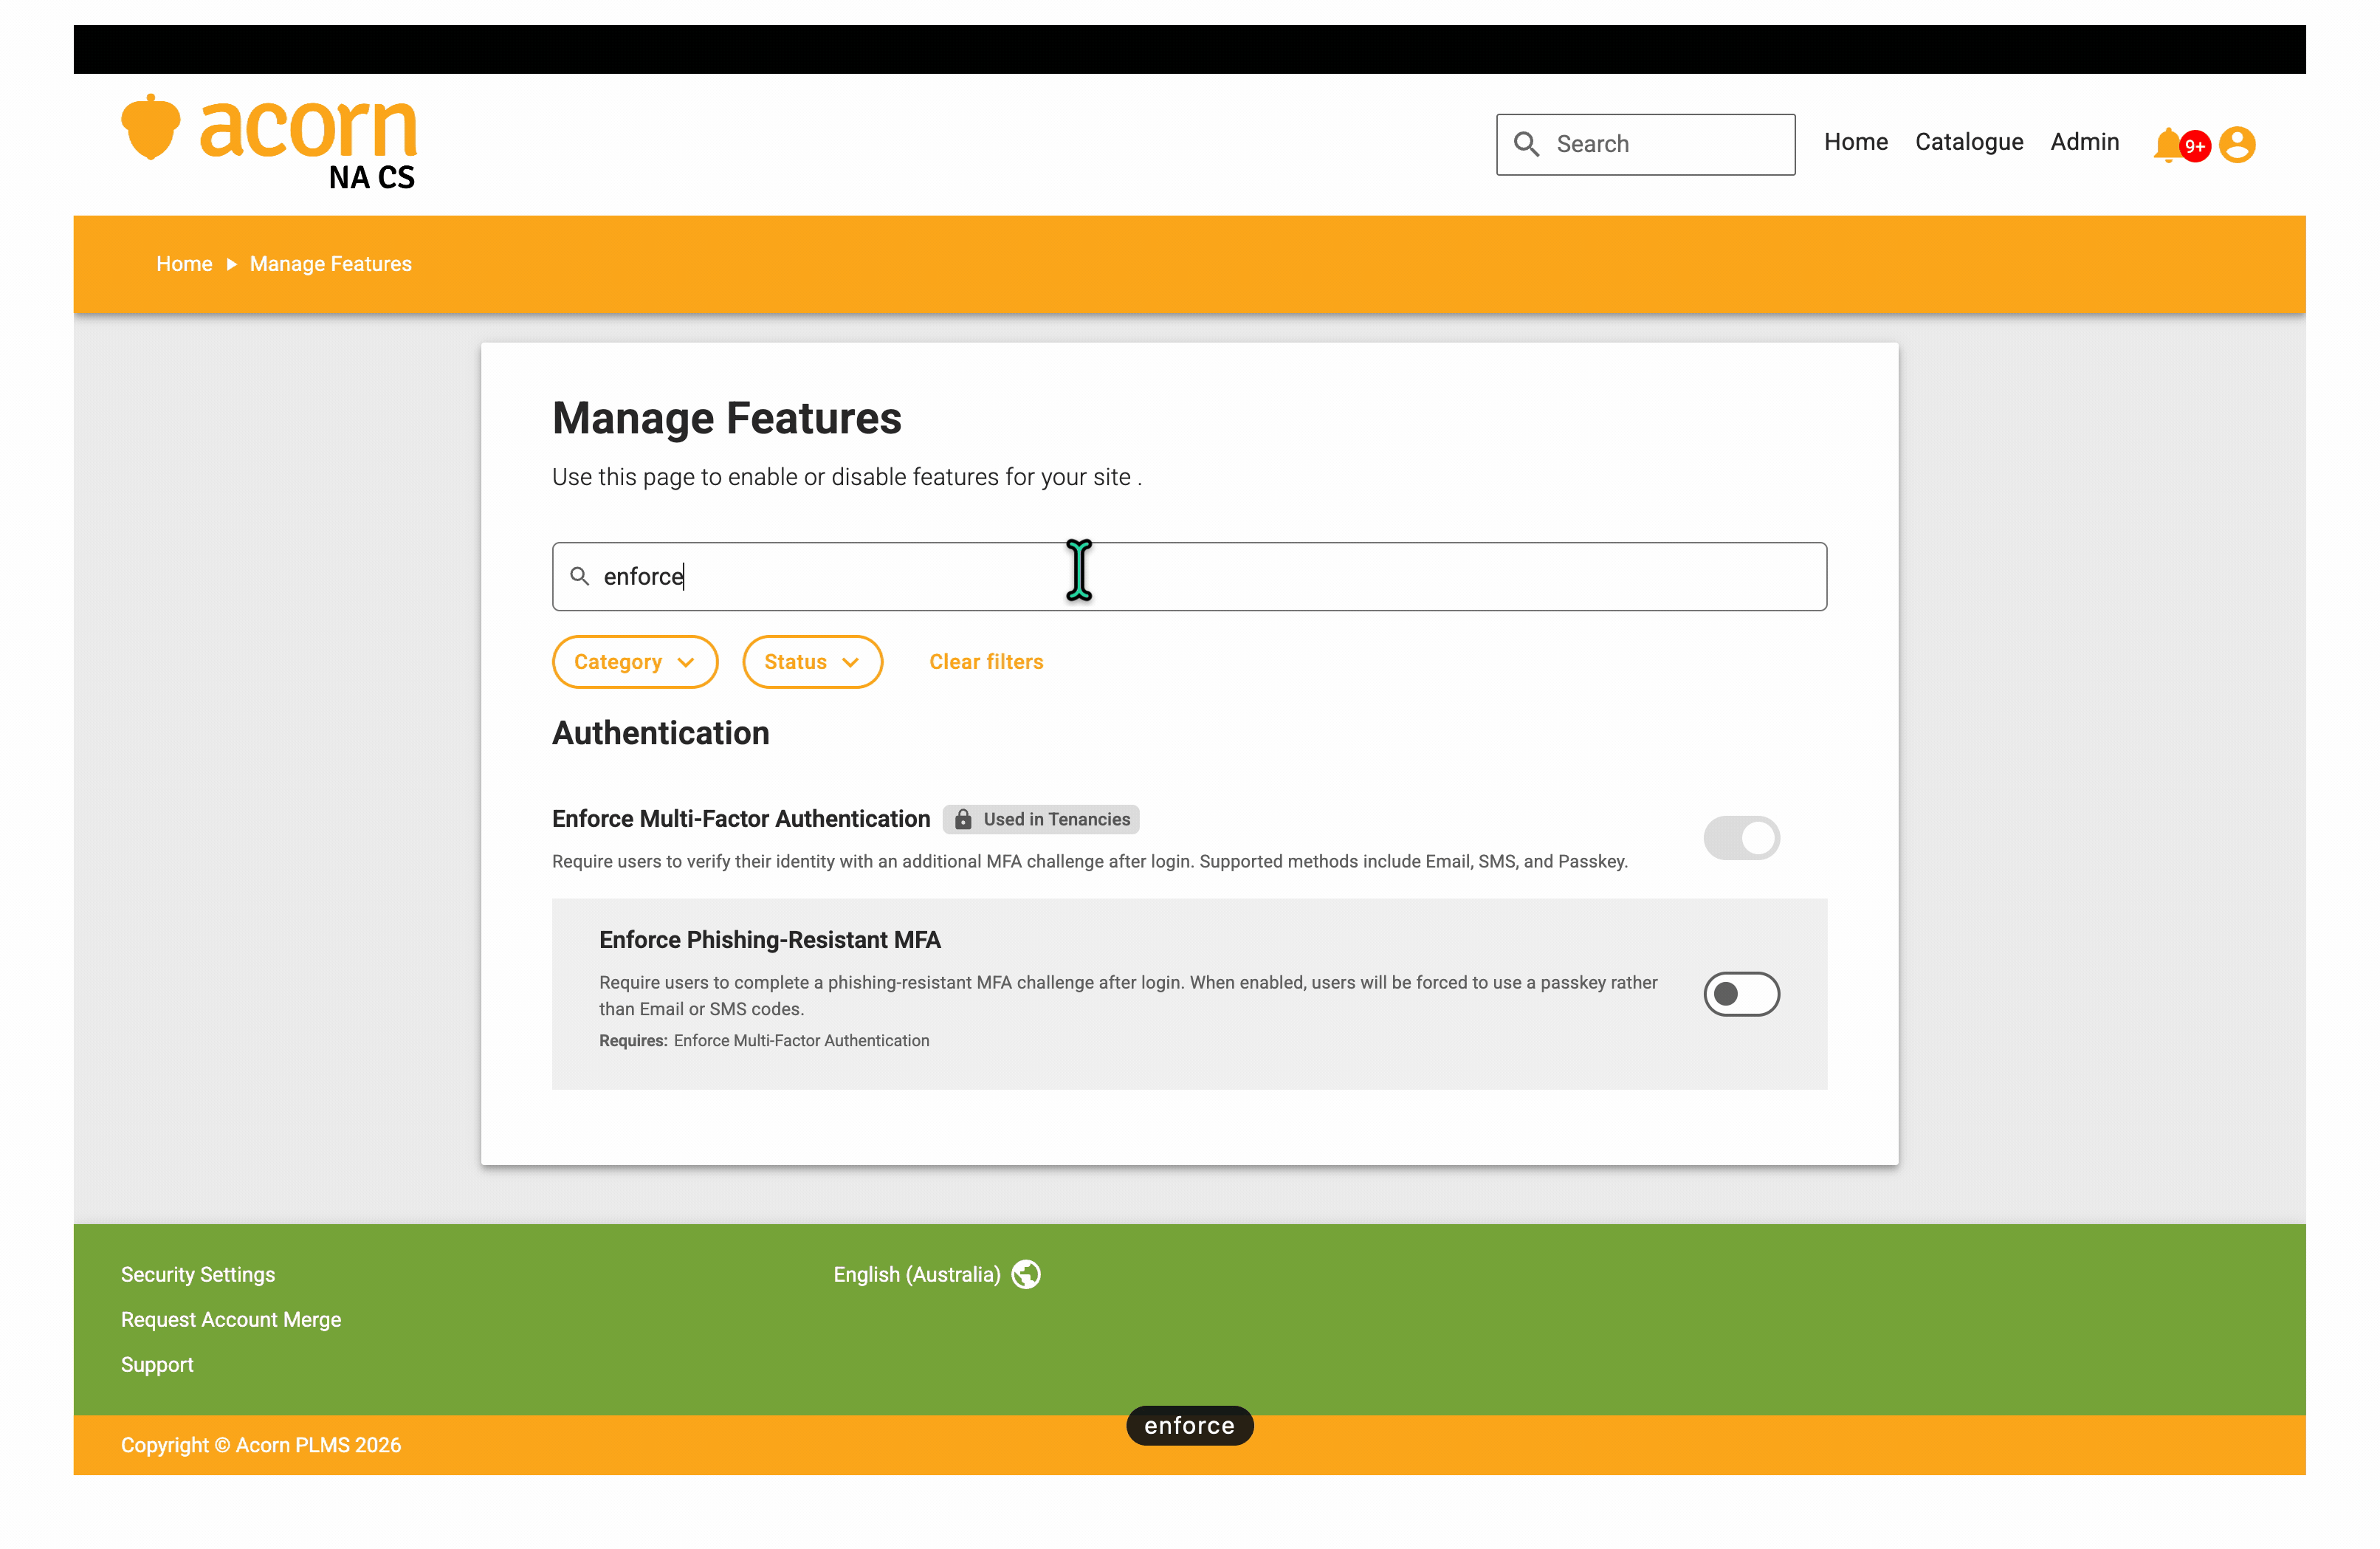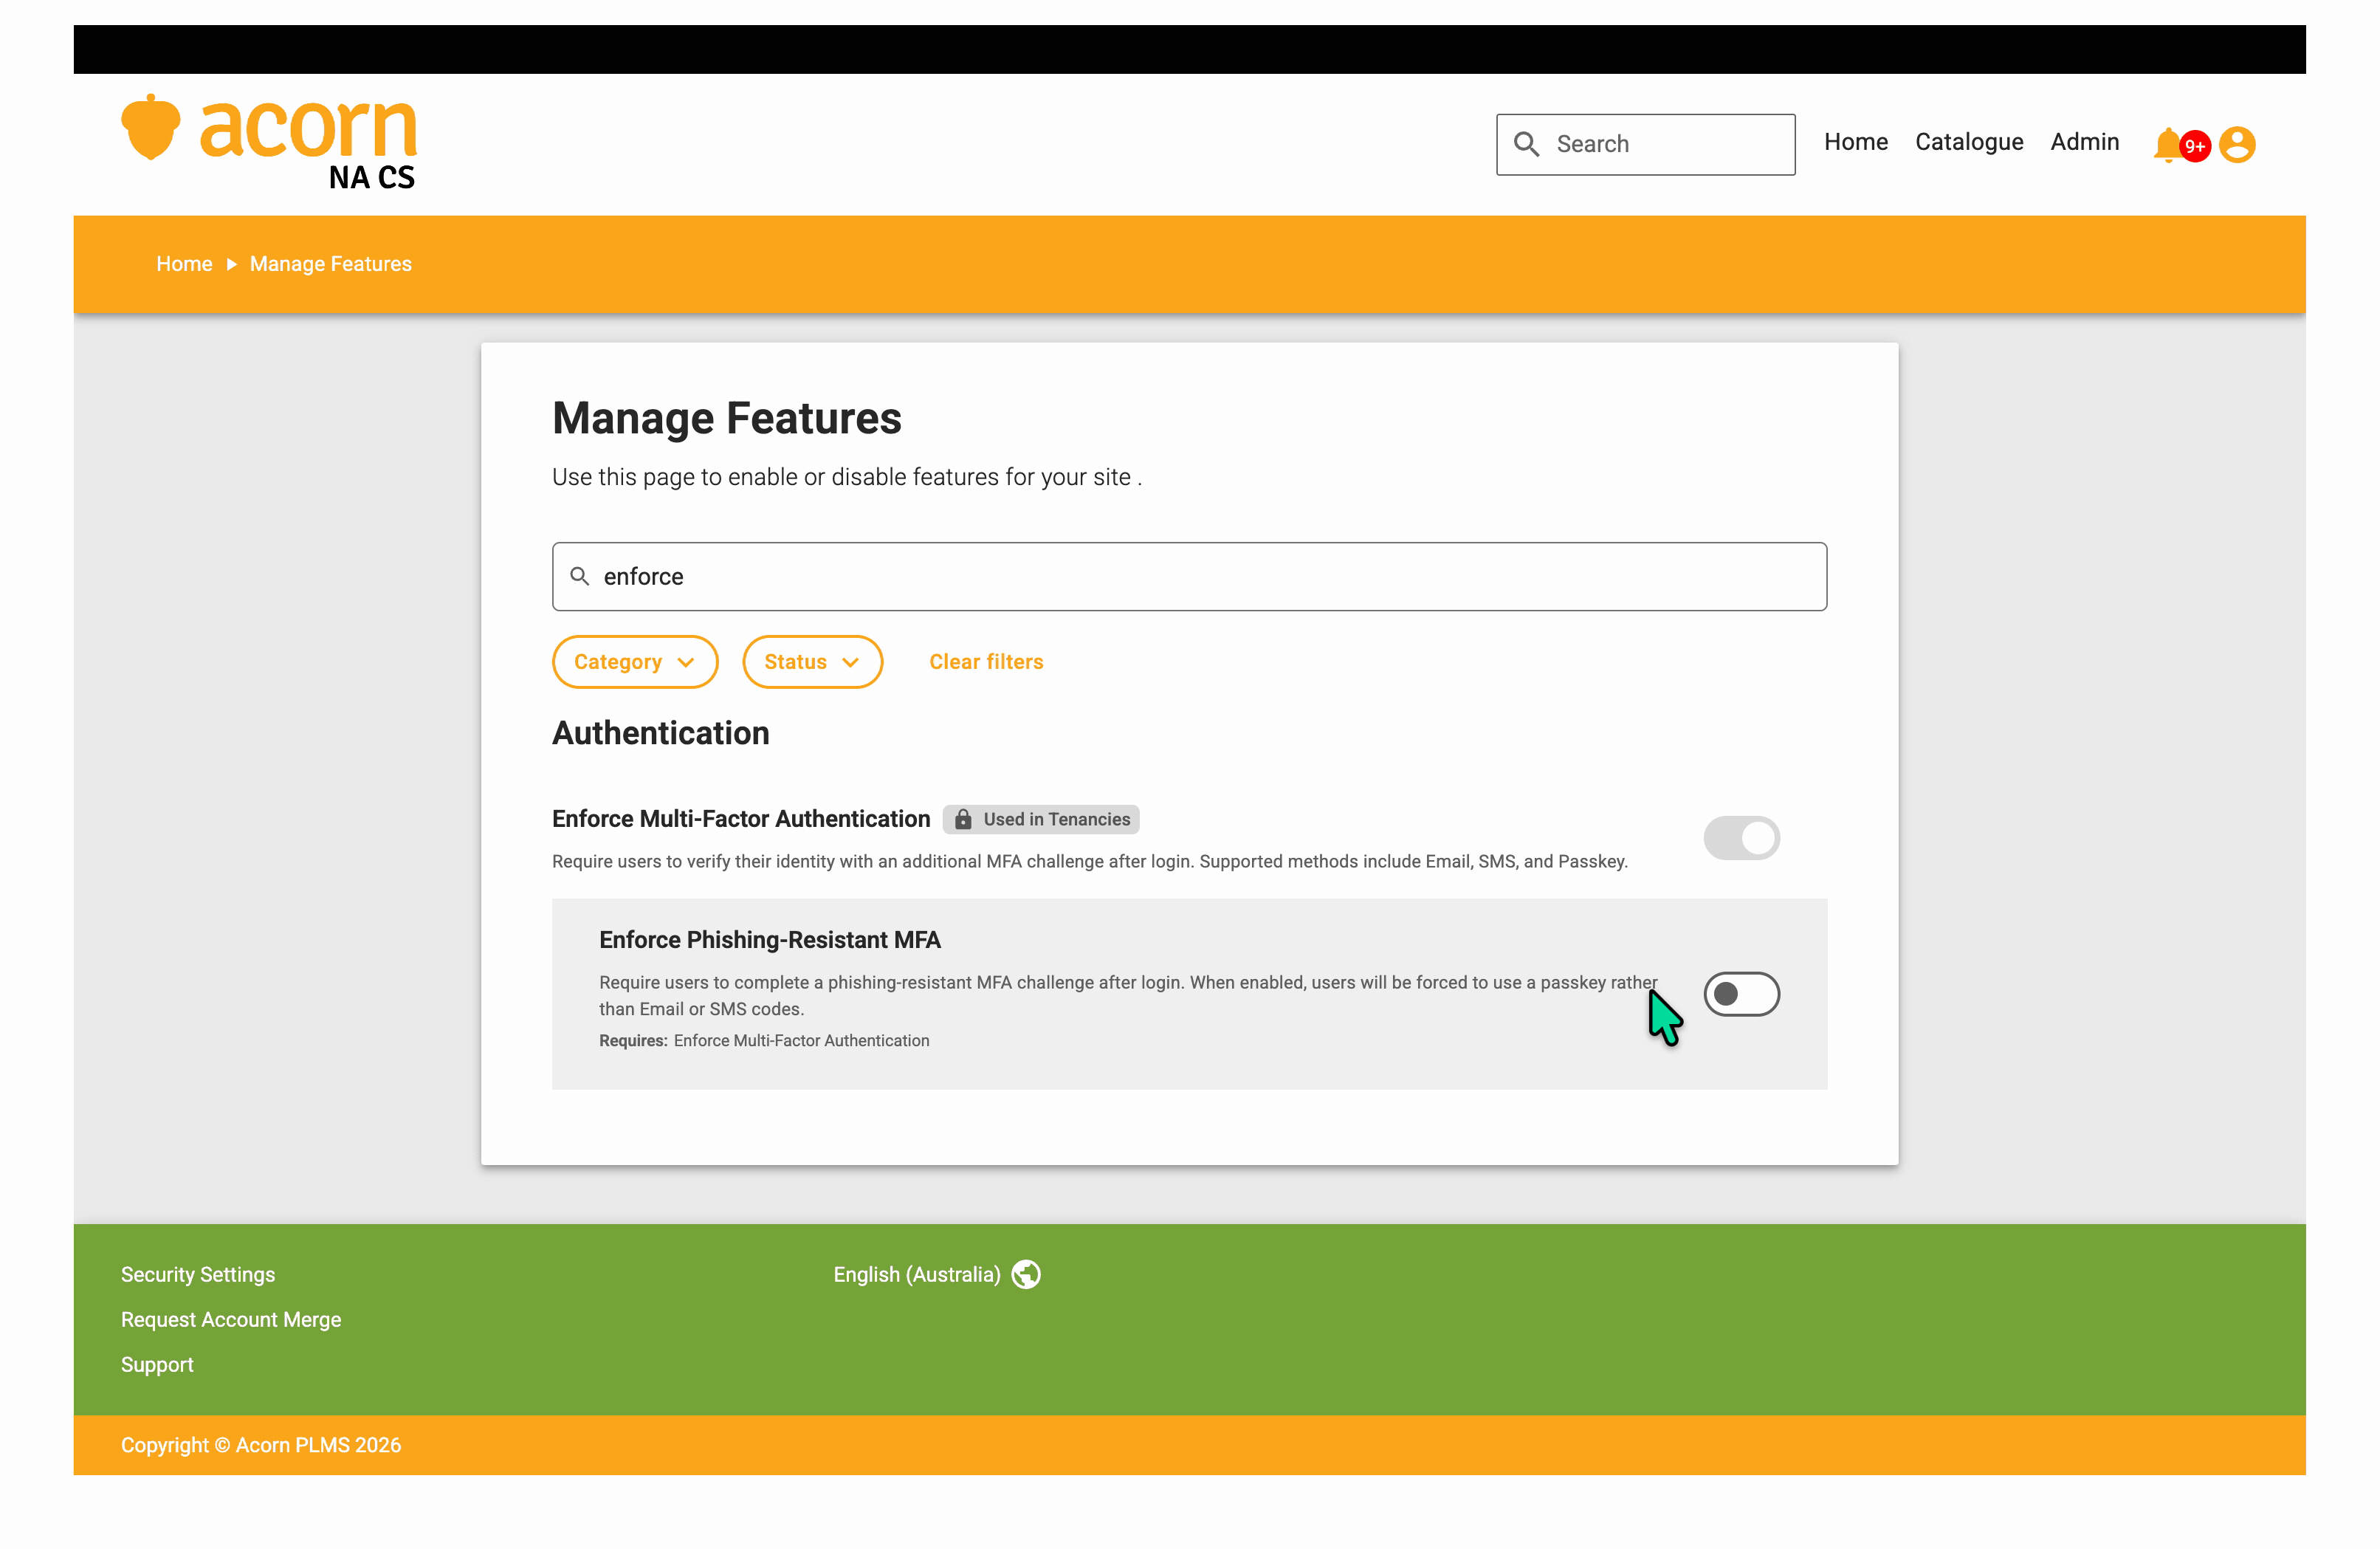
- To force the use of a passkey rather than Email or SMS codes for all users, go to Admin > Administration > Manage Features > Toggle on Enforce Phishing-Resistant MFA.
User MFA setup (first login after MFA enabled)
- The user logs in with their password.
- They are prompted to set up MFA.
- For authenticator app: scan the QR code in Google Authenticator, Microsoft Authenticator, or Authy.
- Enter the 6-digit code from the app to confirm.
- Backup codes are displayed — advise users to save these securely.
MFA for SSO users
If your organisation uses SSO, MFA is typically managed by your Identity Provider (e.g. Azure AD Conditional Access, Okta MFA policies) rather than by Acorn. Contact your IT team to enable MFA at the IdP level.
Troubleshooting MFA issues
- Code not accepted: Ensure the device clock is synchronised (TOTP codes are time-based).
- Lost authenticator app: Admin resets MFA via the Users screen.
- SMS not arriving: Check the phone number in the user profile; check SMS suppression.